
Operating System
Cyber threats evolve daily, but these 10 proven cybersecurity tactics will fortify your digital defenses—from personal devices to enterprise networks. Learn actionable steps to outsmart hackers and protect sensitive data.
Enable Multi-Factor Authentication Everywhere
If you’ve ever wondered why hackers still target passwords despite their flaws, the answer is simple: multi-factor authentication (MFA) turns a single weak link into an impenetrable fortress. Studies show it blocks 99.9% of automated attacks—making it the #1 cybersecurity upgrade you can implement today.
Most platforms (email, banking, cloud services) now offer SMS codes, authenticator apps (like Google Authenticator or Authy), or biometric logins—all with zero cost. Even better, FIDO2 keys (like YubiKey) provide phishing-resistant hardware-based authentication. The key? Enable MFA everywhere—not just your bank, but also social media, work accounts, and even smart home devices.
This isn’t just for tech experts—casual users, small businesses, and developers all benefit equally. Start with the most critical accounts, then roll it out systematically. Your future self will thank you. ⚡
Use Password Managers for Secure Storage
Tired of resetting passwords every few months? A password manager like Bitwarden or 1Password eliminates this headache by generating and storing unique, 30-character passwords for every account—no memorization required.
These tools use AES-256 encryption (the same standard as banks) to secure your vault, while features like biometric login and emergency access sharing add extra layers of protection. They also audit weak passwords and flag reused credentials, reducing your risk of breaches by up to 81%.
Perfect for busy professionals juggling 50+ accounts or anyone frustrated with password fatigue. Start with a free tier and upgrade for advanced features like secure sharing or TOTP support. ✨
Implement Zero Trust Network Architecture
If your business still relies on the old "castle-and-moat" security model, it’s time for an upgrade. Zero Trust Architecture flips the script by assuming every user and device—even inside your network—could be compromised, requiring continuous verification before granting access.
This approach combines identity-based access controls, micro-segmentation, and real-time authentication (like FIDO2 or biometrics) to create a dynamic security posture. Tools like Microsoft Azure AD, Palo Alto Prisma, or Cisco Secure Access make implementation scalable, while continuous monitoring ensures only authorized devices access sensitive resources. The result? A 90% reduction in lateral movement by attackers, according to Gartner.
Ideal for enterprises migrating to cloud-first models or hybrid workforces, Zero Trust eliminates trust assumptions entirely—whether your team works from Denver offices or remote locations. 💪
Regular Software Updates and Patching
Malware exploits one unpatched vulnerability every 4 minutes—and that’s why staying current isn’t optional. Software updates aren’t just about new features; they’re critical security patches that block exploits targeting everything from your laptop to your cloud servers.
Most operating systems (Windows, macOS, Linux) and apps now offer automated updates, but even these can fail if disabled. Enterprise tools like Windows Server Update Services (WSUS) or Patch Management solutions (e.g., ManageEngine, Tanium) let admins enforce updates across fleets. For personal use, enable automatic updates in settings and schedule weekly reboots to ensure pending patches install.
This is non-negotiable for remote workers (where endpoints are prime targets) and small businesses (where breaches often cripple operations). Even gamers should prioritize updates—many ransomware campaigns start with unpatched game clients. ⚡
Deploy Advanced Endpoint Detection Solutions
Sophisticated cyberattacks like ransomware and zero-day exploits often bypass traditional antivirus—so how do you stop threats that evade signature-based detection? Endpoint Detection and Response (EDR) solutions like CrowdStrike Falcon or SentinelOne monitor devices in real-time, using AI-driven behavioral analysis to detect and block attacks before they execute.
These tools go beyond basic scanning by correlating thousands of telemetry points per device, identifying anomalies like unusual process injections or lateral movement attempts. For example, CrowdStrike’s cloud-native architecture delivers sub-second response times, while SentinelOne’s self-healing capabilities automatically roll back compromised files. Many solutions integrate with existing SIEM platforms for centralized threat hunting.
This is a game-changer for organizations with remote or hybrid workforces, where traditional perimeter defenses fail. Even small businesses handling sensitive data should prioritize EDR to stop advanced threats before they cause damage. 💪
Educate Employees on Phishing Attacks
Your employees might be your strongest cybersecurity weak link—70% of breaches start with a phishing email, and most victims never see it coming. Simulated phishing tests and interactive training turn your team from liability into your first line of defense, with platforms like KnowBe4 or PhishMe delivering customizable campaigns that mimic real threats.
These solutions track click-through rates in real time, showing exactly where training gaps exist. For example, a spear-phishing simulation targeting your finance team could reveal who falls for urgent "CEO fraud" requests—then retrain them before real attackers exploit the same tactic. Most organizations see click-through rates drop from 15-30% to under 5% within six months.
Small businesses benefit most from this approach—limited budgets mean every employee must think like a security guard. Start with a quarterly phishing test and follow up with targeted training on the most common scams. 💡
Encrypt Sensitive Data at Rest and Transit
If you handle healthcare records, financial transactions, or even personal tax documents, encryption isn’t optional—it’s a legal shield. Unencrypted data is like leaving your front door unlocked: anyone with access can walk in. Modern encryption transforms readable data into unbreakable code, ensuring only authorized parties can access it—whether stored on your hard drive or transmitted across networks.
For data at rest, tools like BitLocker (Windows) or FileVault (macOS) encrypt entire drives with AES-256, the same standard used by governments. For data in transit, TLS 1.3 (the protocol behind HTTPS) scrambles emails, logins, and file transfers—making interception useless without the decryption key. Compliance standards like HIPAA, GDPR, and PCI DSS mandate these protections, but even individuals should encrypt sensitive files using VeraCrypt for an extra layer of defense.
This is non-negotiable for businesses, but freelancers, remote workers, and privacy-conscious users also benefit. Zero-config encryption (like Apple’s built-in Secure Enclave) means you don’t need a PhD to stay protected. 🔧
Segment Network Traffic with Firewalls
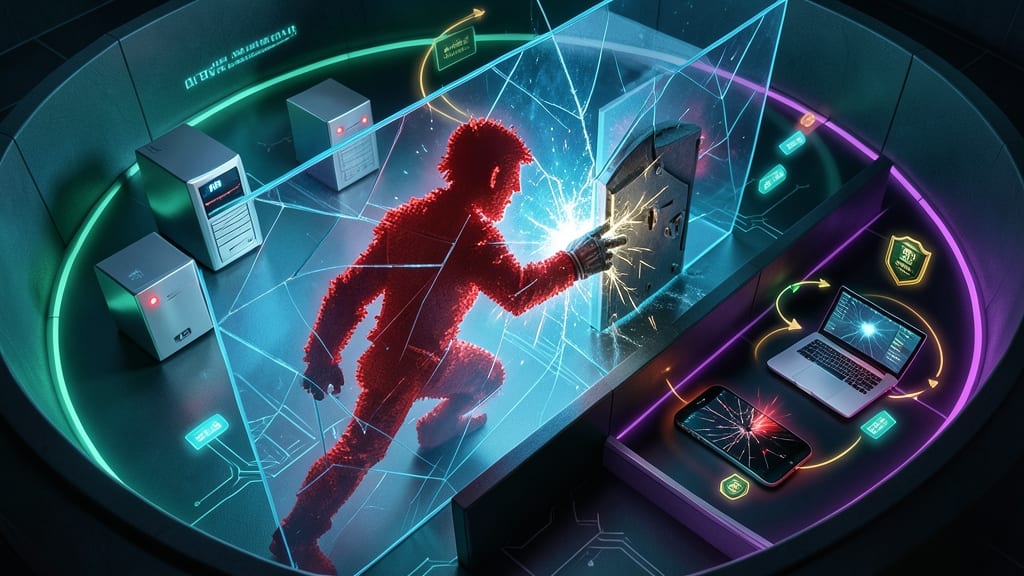
Imagine a hacker breaching your network—now picture them hitting a dead end because your firewall has segmented access like a digital moat. This isn’t just another security layer; it’s a zero-trust strategy in action, where even compromised devices can’t freely move between segments like HR servers and financial databases.
Modern firewalls like Palo Alto Networks or Fortinet let you define rules for traffic between segments (e.g., blocking all east-west traffic by default). Pair that with micro-segmentation, and you’ve created an environment where attackers can’t pivot laterally—even if they bypass one system. The result? Reduced breach impact by up to 75% in tested environments, per Gartner’s 2023 reports.
This approach is a game-changer for businesses with mixed-criticality networks—think healthcare merging patient records with IoT devices. Even home users with smart home setups benefit by isolating cameras from Wi-Fi routers. 💻
Monitor with Security Information Event Management
When security alerts flood your inbox like a digital storm, Security Information Event Management (SIEM) tools like Splunk Enterprise Security or IBM QRadar turn chaos into clarity. These platforms aggregate logs from firewalls, endpoints, and cloud services, then use AI-driven correlation to spot attack patterns before they escalate.
With features like real-time threat scoring and automated incident playbooks, SIEMs prioritize high-risk events—like brute-force attempts or unusual data exfiltration—so your team focuses on stopping breaches, not just monitoring them. Integration with SOAR (Security Orchestration, Automation, and Response) tools further streamlines containment by automating responses to known threats.
Ideal for mid-sized businesses and enterprises, SIEMs transform security teams from reactive firefighters to proactive strategists—especially when combined with existing defenses like firewalls and endpoint protection. 💪
Prepare for Incidents with Response Plans
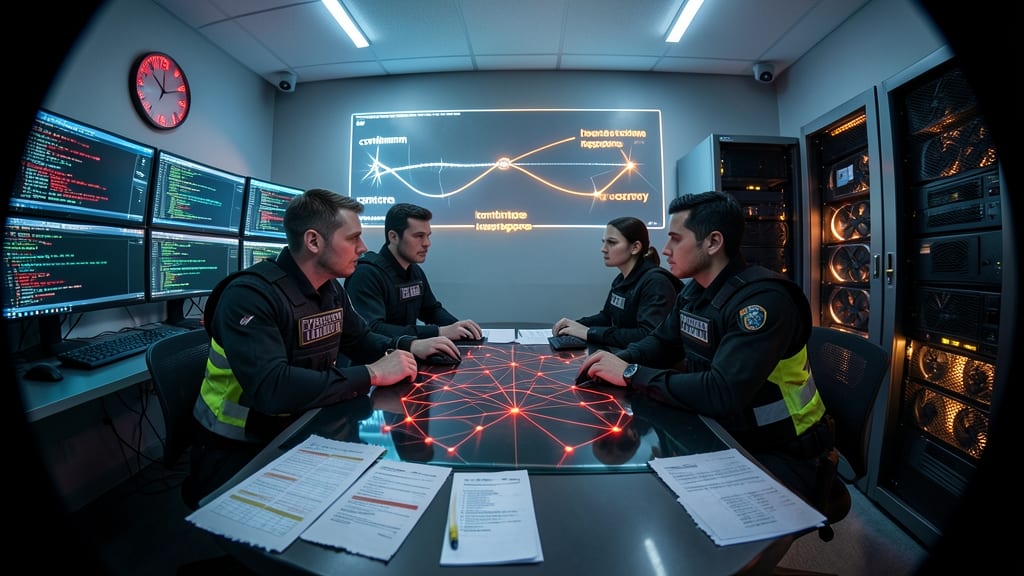
When a breach happens, seconds count—but most organizations scramble without a clear plan. A defined incident response plan turns chaos into action, reducing downtime by up to 70% during critical events. Unlike reactive fixes, these plans map out containment, eradication, and recovery steps before an attack occurs.
Start with a playbook template (like NIST’s SP 800-61) that covers roles, communication protocols, and escalation paths. Document your critical systems, backup procedures, and third-party contacts (e.g., legal, PR, forensics). Tools like Splunk or IBM Resilient automate alert triggers, while tabletop exercises ensure your team practices responses under pressure.
Small businesses often overlook this, but even solo developers should outline steps for ransomware or data leaks. A well-tested plan isn’t just a compliance checkbox—it’s your digital first-aid kit. ✨