
Operating System
Cyber threats evolve daily, but internal safeguards remain your first line of defense. These 10 proven strategies empower cybersecurity leaders to build a robust data protection framework that reduces vulnerabilities and minimizes breach risks—before they escalate.
Role-Based Access Control Implementation
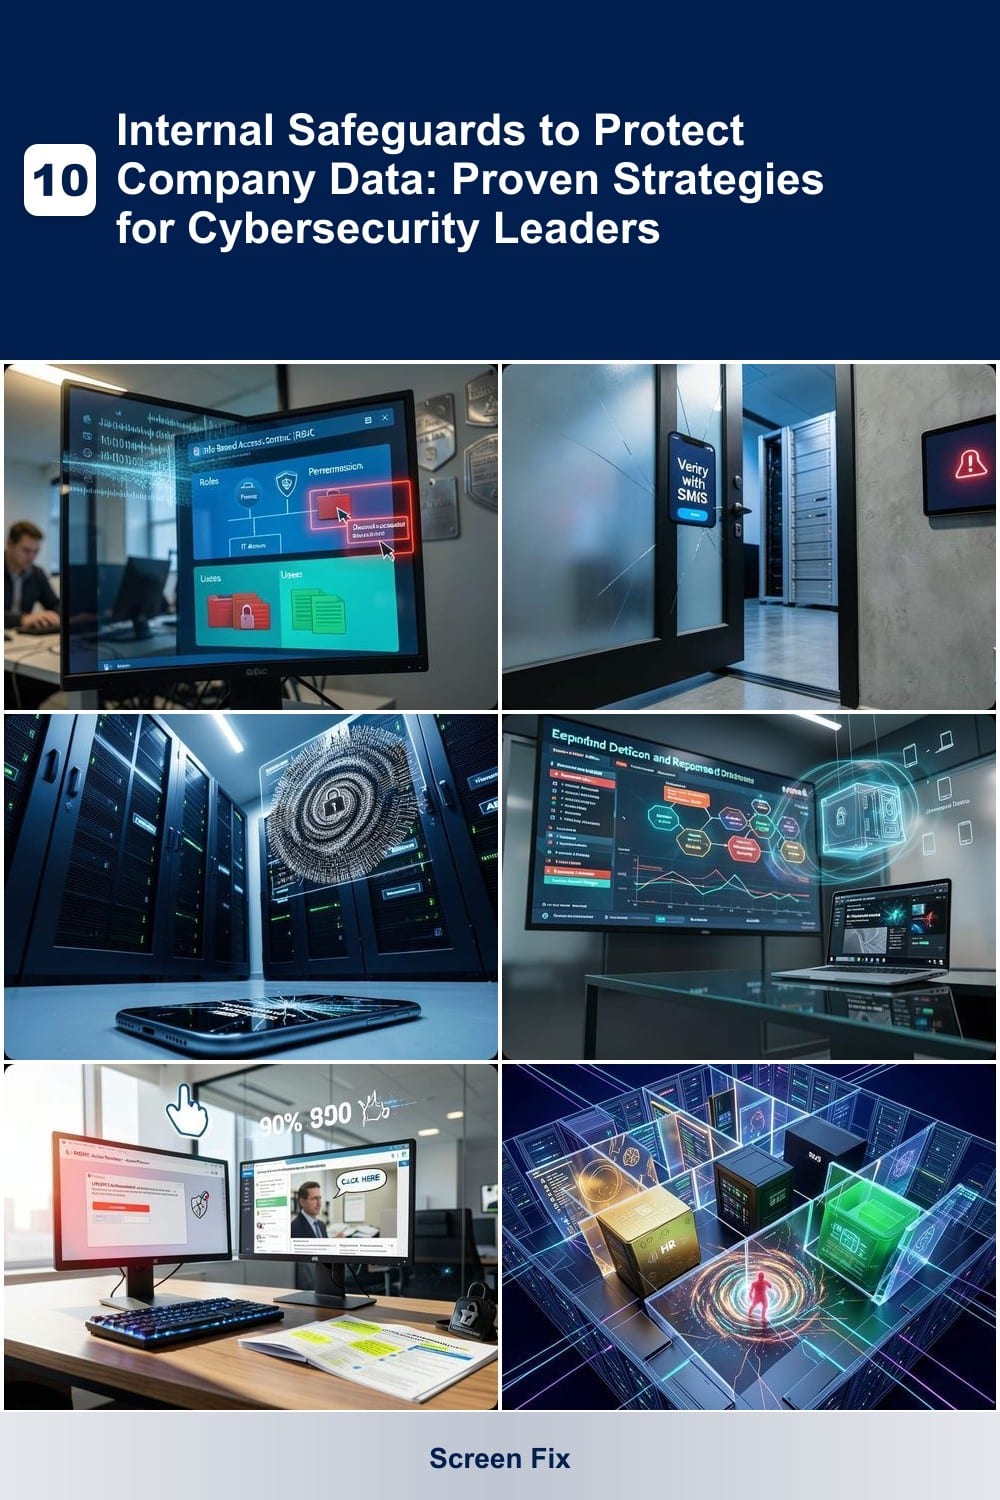
Imagine a scenario where an employee accidentally—or intentionally—downloads sensitive client data they shouldn’t access. Role-Based Access Control (RBAC) stops this before it happens by restricting permissions to only what’s needed for each job role.
With RBAC, you define three key layers: roles (e.g., "HR Manager"), permissions (e.g., "edit payroll"), and users. Tools like Microsoft Azure AD or Okta automate this, ensuring a finance team member can’t modify R&D files. Studies show RBAC reduces insider threat risks by 70% by eliminating excess privileges. Integration with Single Sign-On (SSO) makes adoption seamless.
This is a must for regulated industries (healthcare, finance) or any company with sensitive data. Start with a pilot group to refine roles before rolling out company-wide. 💻
Multi-Factor Authentication Enforcement
Passwords alone are like leaving your front door unlocked—anyone with the right guess can walk in. Multi-Factor Authentication (MFA) adds a second layer of defense, ensuring only authorized users access sensitive internal systems, even if credentials are compromised.
Modern MFA solutions support SMS codes, biometric scans (fingerprint/face ID), or hardware tokens like YubiKey, reducing account takeover risks by 99.9% for high-value targets. Platforms like Microsoft Azure AD, Duo Security, or Google Authenticator integrate seamlessly with existing systems, requiring minimal setup while enforcing compliance with NIST guidelines for secure authentication.
This safeguard is non-negotiable for finance, healthcare, or R&D teams handling regulated data, but even small businesses benefit from the peace of mind it brings. ⚡
Data Encryption for Storage and Transit
Even if your devices are lost or stolen, AES-256 encryption ensures your data stays unreadable without the right keys—whether it's stored in databases, backups, or transmitted across networks. This military-grade standard scrambles data into an unbreakable cipher, making it useless to attackers even if they bypass other security layers.
For storage, tools like BitLocker (Windows) or FileVault (macOS) encrypt entire drives, while cloud providers offer TLS/SSL for transit. Databases benefit from column-level encryption, and email services use S/MIME or PGP for secure messaging. The best part? Most modern systems support these protocols with minimal setup—just enable them and rest easy.
This is non-negotiable for industries handling PHI (healthcare), PII (financial), or trade secrets. Start by encrypting your most sensitive assets first—your legal team will thank you later. ✨
Endpoint Detection and Response Deployment
Remote work expanded your attack surface—but Endpoint Detection and Response (EDR) turns that challenge into an advantage. Unlike traditional antivirus, EDR uses AI-driven behavioral analysis to spot and neutralize threats like ransomware or insider breaches before they escalate, even on unmanaged devices.
Solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint provide real-time monitoring, automated threat containment, and forensic insights to trace attacks back to their origin. They integrate with your existing security stack (SIEM, MFA) and work across Windows, macOS, and Linux—critical for hybrid teams where devices live both in and out of the office.
This is the safeguard that IT admins and security teams deploy to protect laptops, BYOD devices, and IoT endpoints without sacrificing employee productivity. 💻
Regular Security Awareness Training Programs
Most breaches start with a single click—yet 90% of cyberattacks exploit human error, often through phishing or social engineering. Regular security awareness training programs flip the script by turning employees from passive targets into your strongest defense line.
These programs use simulated phishing campaigns (e.g., fake login portals or urgent "CEO requests") to test reactions, followed by interactive modules on spotting red flags like suspicious URLs or impersonation tactics. Platforms like KnowBe4 or Proofpoint automate this with real-time feedback, while gamified quizzes make compliance engaging. The result? Employees recognize threats faster—cutting phishing success rates by up to 70% in organizations that train quarterly.
Ideal for teams handling sensitive data (HR, finance, R&D), these programs are low-cost yet high-impact—especially for SMBs where tech budgets are tight. Start with monthly micro-training (5–10 minutes) to build habits without overwhelming staff. 💡
Network Segmentation for Critical Systems
When a breach happens, the last thing you want is an attacker wandering freely through your network like it’s a buffet. Network segmentation acts as a series of digital walls, isolating critical systems (like HR databases or R&D files) from the rest of your network—so even if one area is compromised, the damage stays contained.
Modern solutions like micro-segmentation (powered by tools such as VMware NSX or Cisco ACI) create granular zones based on application, user role, or data sensitivity. This means a compromised employee device won’t automatically grant access to your financial ledgers or proprietary designs. Studies show segmented networks can reduce breach impact by up to 80% by limiting lateral movement.
This is especially critical for industries handling regulated data (healthcare, finance) or intellectual property. Start with segmenting your most sensitive assets first—then expand as your security posture matures. 💪
Automated Patch Management System
Forget waiting for IT tickets to pile up—automated patch management closes security gaps before attackers can exploit them. Unlike manual updates that get delayed or ignored, these systems scan your entire ecosystem (servers, endpoints, IoT devices) and deploy critical fixes within hours of release, slashing your exposure window to zero-day vulnerabilities by up to 90%.
Modern solutions like Microsoft Intune or Tanium integrate with your existing tools to prioritize patches based on risk level, ensuring mission-critical systems never run outdated software. They also maintain audit trails for compliance, proving you’re proactive—not reactive—during audits. Plus, AI-driven prioritization means high-risk patches (e.g., for ransomware vectors) get deployed first, even in complex environments.
This isn’t just for enterprises—small teams with limited IT staff benefit most, as it eliminates the "update backlog" that leaves systems vulnerable. For companies handling sensitive data, it’s the difference between a breach and a bulletproof defense. ✨
Immutable Backups with Air-Gapped Storage
When ransomware locks your files and demands payment, traditional backups often become hostages too. Immutable backups with air-gapped storage break this cycle by storing copies completely offline and write-protected, ensuring recovery even if your primary systems are compromised.
This approach uses dedicated hardware (like a NAS or external drive) physically disconnected from your network, combined with write-once-read-many (WORM) technology to prevent deletion or encryption. Tools like Veeam or Backblaze automate this process, creating point-in-time snapshots that can’t be altered—critical for compliance with regulations like HIPAA or GDPR.
Ideal for healthcare providers, legal firms, or any business handling sensitive data, this safeguard turns "worst-case scenarios" into mere inconveniences. Your data stays safe even when everything else fails. ✨
Behavioral Analytics for Anomaly Detection
While firewalls and encryption lock down your data, behavioral analytics acts like a silent sentinel—spotting threats you’d never see otherwise. Unlike traditional security tools that react to known attacks, this AI-powered approach learns normal user patterns (like login times, data access habits) and flags deviations in real time.
Solutions like Darktrace or Exabeam analyze thousands of data points per user, detecting anomalies such as unusual late-night logins, sudden large file transfers, or access to systems outside an employee’s role. Machine learning adapts to your organization’s behavior, reducing false positives while catching insider threats or compromised accounts before they cause harm.
This is the ultimate safeguard for industries handling sensitive data—like finance, healthcare, or R&D—where human error or malicious intent can have catastrophic consequences. ⚡
Incident Response Plan with Tabletop Exercises
When a breach hits, every second counts—but most teams freeze. Tabletop exercises turn hypothetical threats into actionable drills, ensuring your team responds like a well-oiled machine. Unlike static plans, these simulations test communication, decision-making, and toolchain effectiveness under pressure, exposing gaps before they become costly mistakes.
Start with quarterly drills (e.g., ransomware containment, data exfiltration scenarios) using tools like MITRE ATT&CK frameworks to map real-world attack paths. Document outcomes in an after-action report, refining roles like IR coordinator or legal liaison for GDPR compliance. The goal? Reduce mean time to detect (MTTD) and contain (MTTC) by 40%—a measurable win for auditors and executives alike.
Ideal for compliance-heavy industries (healthcare, finance) or teams handling sensitive IP, these exercises also build confidence. No more "what-if" paralysis—just battle-tested readiness. ✨