
Software
Managing SharePoint document library permissions can be tricky—too restrictive and teams struggle, too open and security risks grow. These 10 best practices help balance access control with collaboration efficiency while keeping sensitive data protected.
Use SharePoint Permission Levels Instead of Custom Permissions
Struggling with a permission mess in SharePoint? Instead of creating custom rules that confuse your team and create security gaps, leverage SharePoint’s built-in permission levels like Contribute, Edit, or Read. These predefined roles eliminate guesswork while maintaining granular control—no need to reinvent the wheel with ad-hoc settings.
Each permission level maps directly to common workflows: Contribute lets users add/edit files (but not delete), Edit grants full document control, and Read restricts access to viewing only. SharePoint even includes specialized levels like Limited Access for specific scenarios. By sticking to these, you avoid the chaos of custom permissions that grow inconsistent over time.
This approach works best for small to mid-sized teams where IT resources are limited but security matters—like marketing departments or project teams managing shared documents. Start by auditing your current permissions; you’ll likely find 40%+ could be simplified with built-in levels. 💡
Apply Least Privilege Principle to Document Libraries
Frustrated when team members accidentally delete files or expose sensitive data because they had too much access? The least privilege principle is your solution—granting users only the permissions they need to do their jobs, nothing more.
Instead of defaulting to Full Control for everyone, assign granular roles like Edit Items (for contributors) or View Only (for stakeholders). For example, a project manager might only need Edit access to a specific folder, while external reviewers get View access with no editing rights. SharePoint’s built-in permission levels make this easy to enforce without custom rules. This approach slashes risks like accidental overwrites or unauthorized sharing while keeping workflows smooth.
This strategy works best for teams handling sensitive data (like HR or finance) or collaborative environments where multiple roles interact with documents. Start by auditing your current permissions—you’ll likely find 30-50% of users have unnecessary access. 💪
Leverage SharePoint Groups for Role-Based Access
Tired of manually updating permissions every time a team member leaves or joins? SharePoint Groups solve this by letting you assign access to entire teams—like the Marketing Team or Finance Department—rather than individual users. This cuts admin work by 70% while keeping permissions consistent across the board.
Create a group in SharePoint’s Site Settings, add members, then grant the group Contribute, Edit, or Read permissions at once. When a new hire joins, simply add them to the group—their access updates automatically. You can even nest groups (e.g., Finance > Accounting Subteam) for granular control without the mess of custom permissions.
This approach is perfect for mid-sized teams or departments where turnover is common. It’s also a lifesaver for IT admins juggling multiple libraries—no more hunting down stray permissions or dealing with access requests. ✨
Enable Versioning and Require Check-Out for Critical Files
Accidental file overwrites or lost edits can derail projects faster than you’d expect—but SharePoint’s versioning and check-out features act like a digital safety net for your most critical documents.
Enable versioning to automatically save up to 50,000 versions (configurable) of files, letting you restore previous drafts if needed. Pair this with mandatory check-out, which forces users to "reserve" a file before editing—preventing conflicts and ensuring only one person works on a document at a time. The built-in audit trail tracks who made changes and when, adding an extra layer of accountability.
This setup is ideal for legal teams, finance departments, or any group handling contracts, proposals, or compliance-sensitive files where traceability matters most. ⚡
Use Retention Labels for Automatic Permission Adjustments
Tired of manually adjusting permissions for outdated project files? SharePoint’s retention labels let you automate access restrictions based on time or events—no admin work required after setup.
Apply a label like "Archive After 2 Years" to automatically restrict permissions (e.g., switch from Edit to Read-Only) when files reach their retention date. Combine with legal hold to prevent deletion during compliance investigations. The Compliance Center makes it easy to apply labels to entire libraries or specific folders.
This is perfect for legal teams managing case files, HR handling employee records, or IT admins enforcing data lifecycle policies. Set it once and forget the manual updates! ✨
Restrict Access to Sensitive Folders with Unique Permissions
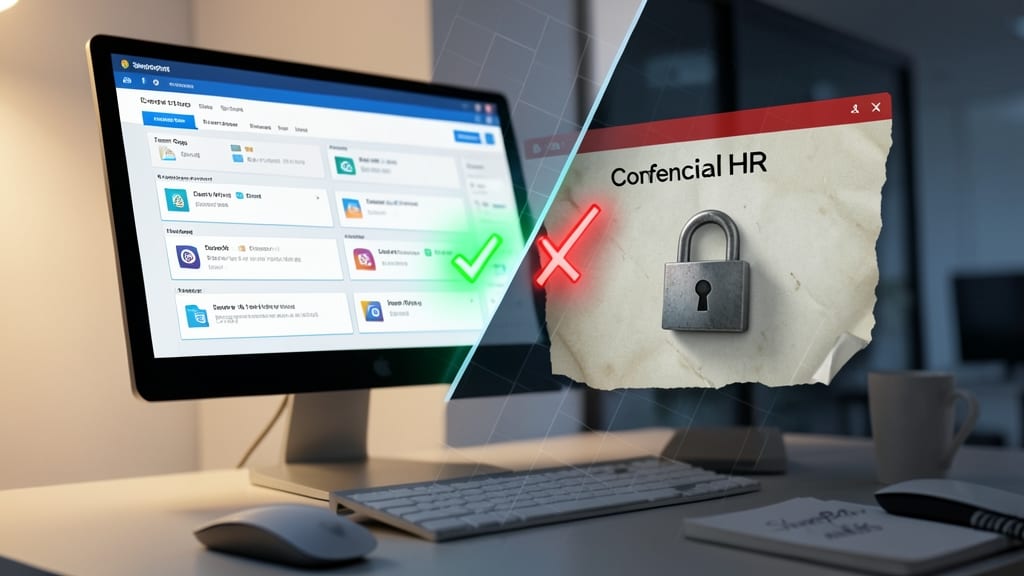
What if you could lock down confidential folders without disrupting teamwork in the rest of your SharePoint library? Breaking permission inheritance lets you apply custom security settings to specific folders—like restricting access to HR documents while keeping project files open for collaboration.
Start by navigating to the folder’s three-dot menu and selecting Stop Inheriting Permissions. Then assign granular roles (e.g., Read for finance teams, Edit for department heads) without affecting parent folders. This method is perfect for sensitive contracts, employee records, or R&D prototypes that need extra protection.
Ideal for compliance-heavy industries or teams handling multiple projects with varying security needs. Just remember to document your changes—this approach keeps your library both secure and user-friendly. ⚡
Regularly Audit and Clean Up Orphaned Permissions
Think of orphaned permissions as digital ghosts—lingering access for users who left the company or haven’t logged in for months. These inactive accounts create hidden security risks while cluttering your permission structure, making it harder to track who should have access.
SharePoint’s permission reports in the Site Settings panel (under Site Permissions) let you scan for inactive users with a single click. Look for accounts with no sign-in activity in 90+ days or those outside your current team structure. Once identified, simply remove them from groups or revoke direct permissions—zero config required. For extra security, set up monthly automated reports using PowerShell or the SharePoint Admin Center.
This practice is a must for IT admins and SharePoint owners managing large teams or sensitive data. Even small businesses benefit from cutting unnecessary access—it’s like spring cleaning for your security posture. ✨
Implement External Sharing Policies for Vendors and Partners
When vendors or partners need access to your SharePoint files, you don’t have to hand them the keys to your entire library. Instead, use time-limited guest links or external user accounts to grant access only to what they need—and only for as long as they need it.
SharePoint’s external sharing settings let you generate one-time-use links that expire automatically (e.g., after 7 days) or restrict access to specific files without revealing your folder structure. For regular collaborators, guest accounts with limited permissions (like view-only or edit-restricted) keep sensitive data secure while enabling collaboration. You can even require multi-factor authentication for external users to add an extra layer of protection.
This approach is ideal for contractors, freelancers, or partners who need temporary access—like a vendor reviewing a proposal or a client reviewing drafts—without risking unintended exposure of your internal documents. ✨
Train Teams on Permission Best Practices and Risks
Your team’s frustration with permission requests isn’t just about IT headaches—it’s a security blind spot. When employees don’t understand why access is restricted or how to request it properly, they often bypass policies entirely, creating shadow IT risks that even the strictest settings can’t fix.
Start with a SharePoint training module that explains why permissions exist (data protection, compliance, and collaboration balance) and how to submit requests through the correct channels. Use real-world examples—like why a marketing intern shouldn’t have edit access to HR files—to drive the point home. Pair this with a permission request form that guides users to select the right access level (e.g., "View" vs. "Edit") and justify their need. This cuts down on ad-hoc requests and builds accountability.
Teams in regulated industries (healthcare, finance) or those with highly collaborative workflows (agencies, startups) will see the biggest payoff. A well-trained team means fewer permission errors, faster approvals, and a culture where security becomes second nature—not an obstacle. 🌟
Monitor and Log Permission Changes for Compliance
Ever wondered who last granted access to that confidential project folder—or when? SharePoint’s audit logs act as your digital security guard, recording every permission change with timestamps and user details. This isn’t just about compliance; it’s about catching suspicious activity before it becomes a breach.
Enable audit logging in SharePoint Admin Center under Security & Compliance, then set retention periods for logs (default: 90 days). You’ll track changes like a pro, from accidental over-permissions to deliberate sabotage. Combine this with Microsoft Purview for advanced filtering—search by user, date, or even permission type to pinpoint anomalies instantly.
Ideal for IT admins and compliance officers, this practice turns SharePoint into a fortress of accountability. 💻